rfunix/tengu
Deployment & DevOps이 페이지는 AI로 자동 번역되었습니다. 기술적인 세부 사항은 원문을 확인하세요. 원문 보기
AI-powered 침투 테스트 MCP 서버
개요
"일본의 신화에서, Tengu는 fierce 산 정신입니다 - 마스터 strategist, warrior, and trainer of samurai. 사이버 보안에서, 그것은 사냥의 모든 단계를 통해 당신을 안내합니다." recon에서 보고하기 — AI-assisted pentesting in one command. Claude를 관통하는 MCP 서버입니다. Nmap에서 Metasploit까지 80개의 보안 툴을 관현했습니다. 내장된 안전 제어, 감사 로깅 및 전문가 보고. - 업계 표준 pentest 도구에 Claude를 연결하는 MCP 서버 - 악용의 통제에서 인간을 유지하면서 자동 재구성 및 스캐닝 - Pentesters, red teamers, 보안 학생 및 컨설팅 회사 - — Nmap, Metasploit, SQLMap, Nuclei, Hydra, Burp-compatible ZAP, 그리고 더 많은 - - Claude는 이전 결과에 근거를 둔 다음 도구를 결정합니다 - 허용 목록, 제한, 감사 로그 및 파괴적인 행동을위한 인간 -in-the-loop - - Correlate 발견 및 전문 pentest 보고서 생성 (MD / HTML / PDF) - - - - Pre-build 신속한 ...
개요(AI 번역)
“일본의 신화에서, Tengu는 fierce 산 정신입니다 - 마스터 strategist, warrior, and trainer of samurai. 사이버 보안에서, 그것은 사냥의 모든 단계를 통해 당신을 안내합니다.”
recon에서 보고하기 — AI-assisted pentesting in one command.
Tengu는 침투 테스트 copilot으로 Claude를 턴하는 MCP 서버입니다. Nmap에서 Metasploit까지 80개의 보안 툴을 관현했습니다. 내장된 안전 제어, 감사 로깅 및 전문가 보고.
- 그것은 무엇입니까? 업계 표준 pentest 도구에 Claude를 연결하는 MCP 서버
- **왜 그것을 사용합니까? ** Automates recon 및 스캐닝은 악의 통제에 있는 인간을 지키기
- 호는? Pentesters, 붉은 팀, 보안 학생 및 컨설팅 회사
키 기능
-80 도구 — Nmap, Metasploit, SQLMap, Nuclei, Hydra, Burp-compatible ZAP, 그리고 더 많은 것
- AI-Orchestrated — Claude는 이전 결과에 근거한 다음 도구를 결정합니다.
- Safety First — 허용 목록, 제한, 감사 로그 및 파괴적인 행동을 위한 인간 접속
- Auto Reports — Correlate 발견 및 전문 pentest 보고서 생성 (MD/HTML/PDF)
이 페이지는 AI로 자동 번역되었습니다. 기술적인 세부 사항은 원문을 확인하세요.
README
원문 README의 일부입니다. 원문 보기.
Tengu — Pentesting MCP Server
“In Japanese mythology, the Tengu is a fierce mountain spirit — master strategist, warrior, and trainer of samurai. In cybersecurity, it guides you through every phase of the hunt.”
From recon to report — AI-assisted pentesting in one command.
Tengu is an MCP server that turns Claude into a penetration testing copilot. It orchestrates 80 security tools — from Nmap to Metasploit — with built-in safety controls, audit logging, and professional reporting.
- What is it? An MCP server that connects Claude to industry-standard pentest tools
- Why use it? Automates recon and scanning while keeping the human in control of exploits
- Who is it for? Pentesters, red teamers, security students, and consulting firms
Key Features
- 80 Tools — Nmap, Metasploit, SQLMap, Nuclei, Hydra, Burp-compatible ZAP, and more
- AI-Orchestrated — Claude decides the next tool based on previous findings
- Safety First — Allowlist, rate limiting, audit logs, and human-in-the-loop for destructive actions
- Auto Reports — Correlate findings and generate professional pentest reports (MD/HTML/PDF)
- 35 Workflows — Pre-built prompts for full pentest, web app, AD, cloud, and more
- 20 Resources — Built-in OWASP Top 10, MITRE ATT&CK, PTES, and pentest checklists
- Stealth Layer — Optional Tor/SOCKS5 proxy routing, UA rotation, and timing jitter
MCP Server Mode (Copilot)
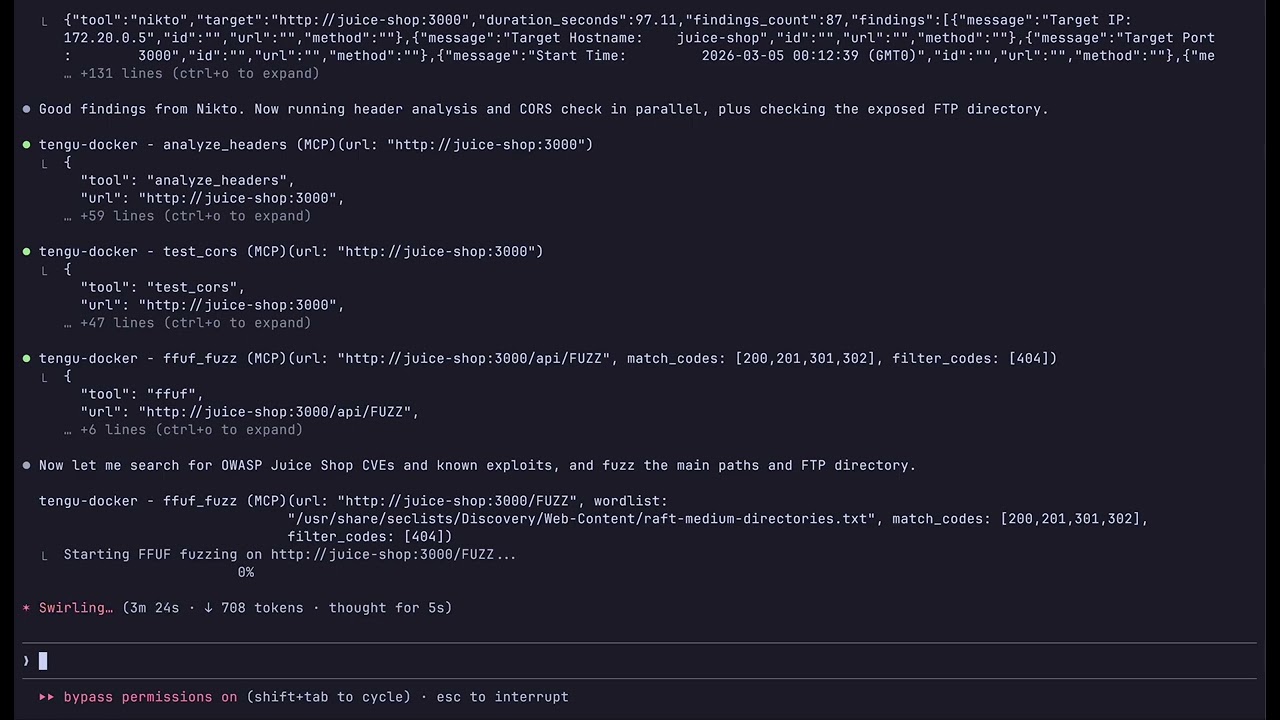
Use Claude as an interactive pentest copilot — you direct the engagement, Claude picks the right tools and chains them together automatically.
Quick Start
git clone https://github.com/rfunix/tengu.git && cd tengu
make docker-build
make docker-up
Connect Claude Code to the running server:
claude mcp add --transport sse tengu http://localhost:8000/sse
Then ask Claude: Do a full pentest on http://192.168.1.100
설치
This server does not publish a one-line install command.
Open the repository installation guide MCP 초보자라면? mcpskill.org 가이드부터 시작하세요 →